Sonatype Nexus Repository 3.95.0 – 3.95.4 Release Notes
The Sonatype Nexus Repository 3.95.x release line includes exciting new features, enhancements, and bug fixes. Learn more in the sections below!
Release Timeline
3.95.0 – August 5, 2026
3.95.1 – August 13, 2026
3.95.2 – August 21, 2026
3.95.3 – August 27, 2026
3.95.4 - September 12, 2026
Check Known Issues Before Upgrading
This version line contains known issues
Before upgrading, see the Known Issues & Upgrade Guidance section at the end of these release notes to determine whether any known issues or upgrade recommendations apply to your environment.
What’s New and Noteworthy in This Release?
The Sonatype Nexus Repository 3.95.x release line includes the following new features and enhancements:
Added Support for Composer Hosted and Group Repositories
Sonatype Nexus Repository now provides hosted and group repository support for Composer, completing its native support for the PHP package ecosystem. In addition to existing proxy repository support, you can now host your own Composer packages, aggregate hosted and proxy repositories into a single group repository, and manage PHP artifacts alongside the rest of your organization's open source and internal components.
For full details, see the Composer Repositories help documentation.
NuGet Hosted, Proxy, and Group Repositories Support Chocolatey Registry and Microsoft Symbol Server
Sonatype Nexus Repository now offers broader support for NuGet ecosystems by adding compatibility with Chocolatey registries and .NET symbol packages. You can now proxy and host Chocolatey packages with NuGet repositories and expose them through group repositories, giving developers a single endpoint for accessing both standard NuGet and Chocolatey packages. This simplifies repository management while making it easier to distribute and consume Windows software packages across your organization.
Nexus Repository also now supports .snupkg symbol packages and the Microsoft Symbol Server Protocol (SymSrv/SSQP), enabling on-demand delivery of Portable PDB (.pdb) files to supported debuggers. Symbol server functionality is available for hosted, proxy, and group NuGet repositories, helping development teams improve debugging workflows while managing application packages and debugging symbols from a single repository platform.
For full details, see the NuGet Repositories help documentation.
Hugging Face Proxy Repositories now Support the Latest huggingface_hub Client Workflows
Sonatype Nexus Repository now supports the latest Hugging Face client workflows by adding compatibility with the /tree/ API endpoint and inbound Bearer token authentication. These enhancements restore compatibility with the official huggingface_hub Python library versions 1.0 and later, including the changes introduced in version 1.22 that require the /tree/ endpoint for snapshot_download() and hf download.
Nexus Repository also supports the Bearer token authentication model used by newer versions of the client, eliminating the need to rely on legacy Basic authentication.
PyPI Proxy Repository Enhancements Improve Compatibility with Private and Version-Specific Repositories
PyPI proxy repositories now support repository-specific URL encoding rules, allowing you to apply format-specific behavior where needed. For example, PyPI repositories that use PEP 440 local version identifiers can encode + as %2B without affecting other repository formats. Existing global URL encoding configurations continue to work unchanged, so no action is required for current deployments.
Nexus Repository also now supports preemptive authentication for PyPI proxy repositories. This enhancement enables successful proxying of private PyPI repositories that do not issue authentication challenges, including GitLab.com-hosted PyPI repositories. Together, these improvements simplify integration with private package registries and help ensure more reliable access to Python dependencies across diverse repository implementations.
Improvements to the Nexus One UI
The Nexus One UI includes a broad set of usability, accessibility, and reliability improvements across core workflows. This release completes support for task management in the Nexus One UI, allowing you to configure, schedule, run, monitor, and manage all supported task types without switching to the legacy interface. Task configuration forms now provide a more consistent experience across task types while preserving compatibility with existing task definitions. Configuration created in either interface remains synchronized, making it easier to transition between experiences during adoption.
This release also improves the overall Nexus One UI experience with refinements to navigation, search, dashboard, browsing, and user management workflows. Updates include improved accessibility, more consistent interface behavior, clearer feedback throughout common tasks, and continued modernization of the underlying UI architecture. Together, these enhancements provide a more polished and reliable experience while establishing a stronger foundation for future Nexus One UI improvements.
Amazon ECR Proxy Repositories Now Support Temporary AWS Credentials
Sonatype Nexus Repository now supports temporary AWS credentials for Amazon ECR proxy repositories, making it easier to authenticate with modern AWS identity services. You can now configure an optional AWS session token alongside your AWS access key and secret key, enabling authentication with credentials issued by AWS Security Token Service (STS) and AWS IAM Identity Center (SSO). Existing configurations that use long-lived AWS access keys continue to work without changes.
Expanded Instance Migrator Support for Ansible Galaxy, OCI, and Terraform (Instance Migrator 1.1.28)
Sonatype Nexus Repository Instance Migrator release 1.1.28 adds support for Ansible Galaxy and OCI formats, expanding the range of repository formats you can include when moving content between Nexus Repository instances. This enhancement helps reduce manual migration work when your environment includes these formats.
Instance Migrator also adds support for Terraform state files. You can now use Terraform-managed state directly as a migration source, making it easier to migrate environments that rely on Terraform for infrastructure management without first converting or manually preparing the state data.
Firewall Success Metrics Dashboard
Sonatype Repository Firewall now includes a new Firewall Success Metrics dashboard in Enterprise Reporting, giving organizations a clearer understanding of how effectively Firewall protects their software supply chain. By bringing key operational and security insights together in one place, the dashboard helps teams measure the impact of their security policies, identify trends in component risk, and determine whether quarantine workflows are reducing exposure to malicious or vulnerable components. At a glance, teams can monitor metrics such as component evaluations, quarantines, malicious component detections, waivers, and quarantine response times to understand how Firewall is performing over time.
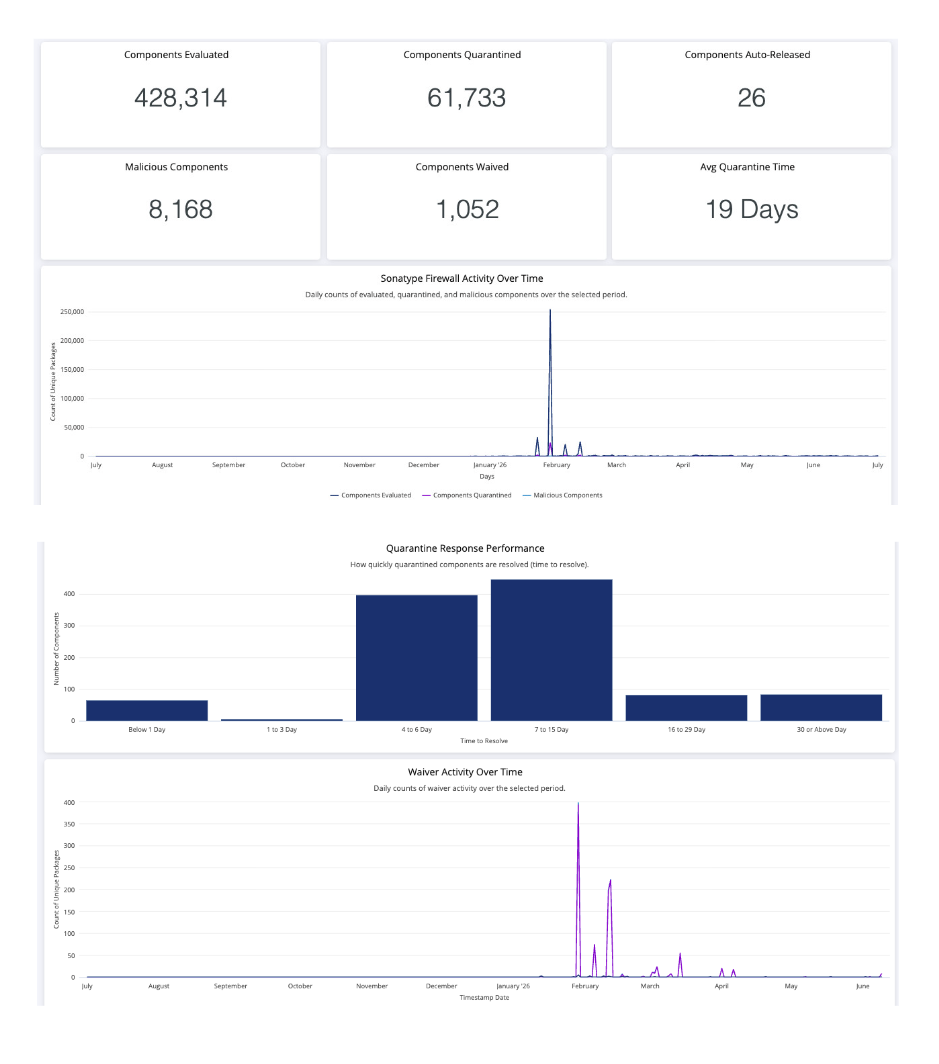 |
With greater visibility into Firewall activity, security, platform, and engineering teams can make more informed decisions about policy tuning, prioritize response efforts, and demonstrate the value of their software supply chain security program. Interactive filtering and detailed reporting make it easier to investigate quarantine trends, understand why components are blocked, monitor waiver usage, and identify opportunities to reduce review times and continuously improve how open source risk is managed across the organization.
For full details, see the Firewall Success Metrics Dashboard help documentation.
Configure the Firewall for Docker Layer Download Timeout
Sonatype Nexus Repository now lets you configure the timeout used by Firewall for Docker when downloading container image layers during policy evaluation. Previously, this timeout was fixed at 10 minutes, which could prevent image evaluation from completing in environments where legitimate network conditions, such as proxy-based antivirus scanning or other network inspection, significantly increase download times. You can now adjust the timeout to up to 240 minutes by setting the nexus.firewall.container.download.timeout.minutes system property to better accommodate your environment while maintaining Firewall for Docker protection for large or slow-to-download images.
Cleanup Policy Enhancements
Note
A known issue with the Retain last N versions cleanup policy was fixed in Nexus Repository 3.95.4 and 3.96.1.
Nexus Repository provides more flexible cleanup policy management to help control repository growth across a wider range of package formats. The Retain last N versions capability is now available for all versioned repository formats that support version semantics. For the newly supported formats, this capability is available exclusively in the Nexus One UI.
Note also that this feature requires a Pro license and self-hosted deployments must use a PostgreSQL database. It is not supported for H2 databases or in Community Edition deployments.
Supported formats include:
Apt
Docker
Go
Helm
Maven
npm
NuGet
Pub
PyPI
RubyGems
Swift
Terraform
Yum
This enhancement helps organizations with high-volume CI/CD pipelines manage storage growth consistently across repositories without relying on custom automation.
Cleanup policy administration is also more streamlined. You can now assign a cleanup policy to multiple repositories directly from the policy configuration, view associated repositories in one place, and preview cleanup behavior across those repositories without editing each repository individually.
In addition, Nexus Repository introduces new cleanup policy REST API functionality for targeted cleanup execution, allowing you to run cleanup for a single repository on demand. The API supports synchronous dry runs that report the number of matching components and asynchronous cleanup execution with status tracking, giving administrators greater control over cleanup operations while avoiding repository-wide scheduled runs.
Bug Fixes
The tables below detail notable bug fixes in each release within this release line.
3.95.4 Bug Fixes
Issue ID | Description |
|---|---|
NEXUS-54915 | The Retain N versions cleanup policy now uses correctly normalized component versions when ranking pre-release components, preventing newer versions from being selected for deletion while older versions are retained. |
3.95.3 Bug Fixes
Issue ID | Description |
|---|---|
NEXUS-54717 | Sonatype Nexus Repository now updates the lastDownloaded timestamp for Docker manifest HEAD requests, preventing actively used images from being incorrectly targeted by cleanup policies. |
3.95.2 Bug Fixes
Issue ID | Description |
|---|---|
NEXUS-54576 | NuGet hosted repositories with Disable Redeploy now correctly allow new packages to be published even when those packages share common third-party PDB files with previously uploaded packages. Regular packages containing embedded PDBs are no longer misfiled as symbol packages. |
NEXUS-54572 | NuGet symbol assets ( |
NEXUS-54550 | Docker proxy repositories backed by Amazon ECR now accept pre-generated ECR authorization tokens (obtained via |
3.95.1 Bug Fixes
Issue ID | Description |
|---|---|
NEXUS-54440 | Nexus Repository now falls back to the cached PyPI JSON index when the HTML index does not contain a requested package file. |
NEXUS-54371 | Nexus Repository now re-queries the upstream source for NuGet V2 |
NEXUS-54336 | Nexus Repository now limits manifest scanning during Docker proxy tag requests, preventing download delays in repositories with large numbers of SHA-256 manifests. |
NEXUS-54250 | Fixed malware risk banner display behavior in the Nexus One user interface. |
NEXUS-54143 | Nexus Repository now completes blob store group member removal without repeatedly reprocessing blobs with missing |
3.95.0 Bug Fixes
Issue ID | Description |
|---|---|
NEXUS-54092 | Terraform module downloads from hosted repositories now succeed for all valid archive formats (.tgz, .tbz2, and .txz), including modules with standard semantic version numbers such as 4.1.1. |
NEXUS-54089 | Cosign signing and attestation against Docker hosted repositories with large numbers of manifests now complete in seconds, thanks to a database path index and a scan cap that prevents exhaustive manifest searches during metadata propagation. |
NEXUS-54023 | Users with the |
NEXUS-53975 | Terraform proxy repositories now support a "Use pre-emptive authentication" option, enabling credentials to be sent on the first request to an upstream Nexus instance rather than waiting for a challenge header that never arrives. |
NEXUS-53923 | During upgrades, the asset blob reference migration check runs as a lightweight background task after startup rather than as a blocking scan on the main startup thread. |
NEXUS-53898 | The copy button in the classic UI Browse › Repositories URL column now opens the copy dialog correctly, allowing repository URLs to be copied to the clipboard. |
NEXUS-53883 | Components moved via staging operations retain their normalized version data, allowing Docker cleanup retain-n policies to evaluate and remove eligible components correctly. |
NEXUS-53874 | Dart/Pub hosted repositories now accept package names beginning with an underscore (for example, _my_private_package), aligning with the official pub.dev specification. |
NEXUS-53833 | Browsing the /simple/<package>/ index on PyPI hosted repositories no longer writes blob files to the blob store on each request, eliminating spurious updated-uploaded audit events and uncontrolled disk growth between Compact Blob Store task runs. |
NEXUS-53830 | Docker layer uploads to Azure blob store repositories now use Azure server-side copy for single-chunk transfers, eliminating the redundant download-and-re-upload cycle that previously caused large layers to take roughly twice as long to push. |
NEXUS-53828 | Transient GCS 503 backend errors encountered during blob attribute writes in doDelete() are now retried with exponential backoff, allowing Docker uploads and similar operations to complete successfully instead of failing immediately. |
NEXUS-53826 | Terraform, Ansible Galaxy, and Swift hosted repositories no longer cache "not found" responses, so post-upload verification requests correctly return the uploaded asset instead of a stale 404. |
NEXUS-53816 | Concurrent repository deletions now complete successfully without leaving repositories in an unrecoverable STOPPED state that previously required a full restart to resolve. |
NEXUS-53778 | Requests carrying a structurally invalid Authorization: Basic header—such as an unexpanded ${NPM_TOKEN} placeholder in an npm .npmrc or CI config—now receive an HTTP 400 Bad Request response instead of 401. |
NEXUS-53755 | The top-level search More Criteria menu now includes Name and Version fields at the generic level, allowing users to filter search results by version across all package formats without navigating into format-specific sections like Composer Repositories. |
NEXUS-53733 | PyPI proxy repositories now send the correct upstream ETag in outbound If-None-Match headers, allowing PyPI to return 304 Not Modified responses instead of forcing full re-downloads, and no longer write a new blob to the blob store on every simple index request. |
NEXUS-53719 | Permission checks for users authenticated through external realms (SAML, LDAP, Crowd, OAuth2) now resolve role-to-permission mappings a single time per login rather than once per privilege checked, eliminating the ~20-second UI load delay experienced by users with large role sets. |
NEXUS-53697 | NuGet hosted repositories now return 206 Partial Content with correct Content-Range headers when clients request byte ranges, eliminating full-package downloads for partial-content requests against local blob stores. |
NEXUS-53670 | R proxy repositories now correctly handle CDN-prefixed content-addressable archive names from r-universe and R-multiverse, and the R-multiverse pollinator resolves package details dynamically from the live index rather than relying on hardcoded versions. |
NEXUS-53606 | Improved JAX-RS client error logging to reduce noise in server logs. |
NEXUS-53599 | Blob store metrics—including BLOB COUNT and USED SIZE—are preserved correctly when a blob store is promoted to a group, eliminating the need to manually run the Recalculate Blob Store Storage task. |
NEXUS-53586 | The Source dropdown selection in Settings > Security > Users is now preserved after deleting a user, keeping the filtered list on the selected realm instead of reverting to Local. |
NEXUS-53571 | Requests carrying a malformed Base64 Authorization header now receive a 401 Unauthorized response instead of an HTTP 500 error. |
NEXUS-53496 | Ansible Galaxy hosted repositories now return HTTP 409 Conflict (instead of 400) with a Galaxy-compatible duplicate-version error body when a duplicate collection version is published to a write-once (ALLOW_ONCE) repository; clients that explicitly expected HTTP 400 for this case should be updated. |
NEXUS-53492 | PyPI group repositories now serve a single authoritative index entry per filename, giving hosted members precedence over proxy members so pip 26's hash verification receives consistent checksums and installs patched components successfully. |
NEXUS-53476 | Existing cached .whl.metadata assets are automatically migrated to application/octet-stream on upgrade, and PyPI proxy repositories now serve .whl.metadata files with the correct content type to prevent WAF rejections and checksum mismatches. |
NEXUS-53468 | Terraform proxy repositories now correctly resolve components from providers with long alphanumeric namespaces without misidentifying the namespace as an authentication token. |
NEXUS-53463 | PyPI group repositories automatically invalidate their cached index when Sonatype Repository Firewall (PCCS) filtering is toggled for any member proxy, ensuring all available package versions are served immediately. |
NEXUS-53458 | The Settings → Repositories page loads in normal time during post-upgrade blob-size copy task execution because task completion checks now cache negative results for 30 seconds. |
NEXUS-53457 | The "Secrets - Migrate secrets" upgrade task now completes successfully for repositories that reference non-existent cleanup policies, automatically removing stale policy names during upgrade. |
NEXUS-53394 | Transient GCS 503 backend errors during Compact Blob Store operations are now retried with exponential backoff, and compaction tasks that fail to hard-delete blobs correctly report as failed. |
NEXUS-53383 | Pub package uploads now consistently identify the root pubspec.yaml as the authoritative metadata source regardless of archive entry order. |
NEXUS-53373 | Telemetry script fetches in air-gapped environments now time out within a configurable window (default 5 seconds) instead of blocking the UI for up to 80 seconds, with stale cached content served as a fallback. |
NEXUS-53343 | Repository search indexes remain queryable throughout the "Repair - Rebuild repository search" task, with orphaned records cleaned up only after re-indexing completes. |
NEXUS-53338 | Pull replication now bypasses the proxy staleness check for modified assets, ensuring updated content is fetched immediately from the source. |
NEXUS-53317 | Stale repodata entries in the browse tree of YUM group and proxy repositories are automatically removed when merged metadata is regenerated. |
NEXUS-53306 | The Preview UI Firewall column now accurately displays each proxy repository’s protection state and violation counts, matching the configured Quarantine, Audit, or Unprotected status. |
NEXUS-53300 | NuGet v3 hosted repository query results are now correctly returned for users whose Content Selector privilege includes a path condition on PostgreSQL deployments. |
NEXUS-53265 | Mixed unparenthesized |
NEXUS-53263 | Components remain visible in search results for users with Repository Content Selector privileges after tag association, allowing repeated tag associations to succeed without requiring broader repository privileges. Repositories where components were updated via incremental indexing (for example, tag association) while running an earlier Nexus Repository version may require a search index rebuild after upgrade to 3.95.0 in order to restore visibility for users who rely only on Repository Content Selector privileges. |
NEXUS-52995 | When PCCS age-based policy filtering quarantines npm package versions, diagnostic logging now captures the catalog date and policy condition details for each affected version. |
NEXUS-52942 | Pagination Link headers for Docker group repositories accessed via repository URL path now correctly reference the group repository path rather than the internal member proxy path. |
NEXUS-52934 | Assets in group repositories remain accessible throughout a Change Repository Blob Store migration because source blobs are retained until database references are fully updated. |
NEXUS-52826 | Group repositories now display an aggregated Firewall Report status based on their proxy members, and the Firewall Report column header is correctly marked as non-sortable. |
NEXUS-52283 | The Hugging Face proxy now implements the /tree/{revision} endpoint, enabling snapshot_download() and hf download to work with huggingface_hub 1.22.0+ even for repositories with more than 1,000 files. |
NEXUS-52176 | IQ Server connection failures now return actionable error messages instead of the previous generic compatibility message. |
NEXUS-51938 | All nodes in an HA cluster now immediately evict their shared HTTP connection pool when proxy or other HTTP client settings change. |
NEXUS-51661 | Trailing wildcard searches with fewer than three characters before the wildcard now return HTTP 400 with a clear error message instead of silently returning empty results. |
NEXUS-51526 | The Repair - Data Repair Plan task now removes orphaned database records for assets whose .bytes file is missing when "Keep db records" is unchecked. |
NEXUS-51524 | The Repair - Execute Data Repair Plan task now displays the complete plan count by retrieving aggregated statistics from a new server-side summary endpoint. |
NEXUS-51451 | Conan proxy repository search now returns cached results successfully when the remote is manually blocked instead of returning a 500 error. |
NEXUS-51368 | Raw repository searches by filename now return correct results when the filename contains a period character. |
NEXUS-50783 | Removing a member from a Maven group repository now completes quickly, with orphaned asset cleanup running in the background. |
NEXUS-37620 | The Repair - Rebuild Maven repository metadata task now regenerates missing checksum files for maven-metadata.xml when checksum rebuilding is enabled. |
NEXUS-33892 | Group repository caches are automatically invalidated when routing rules are assigned, removed, or modified on any member proxy repository. |
NEXUS-29245 | npm dist-tag add and npm dist-tag rm commands now work against group repositories by delegating tag operations to the configured writable member repository. |
NEXUS-29099 | Task log file handles are now released immediately upon task completion, preventing accumulation of open file descriptors. |
NEXUS-28581 | When thread cooperation limits are exceeded during high-concurrency NuGet proxy requests, logs now emit a detailed warning message identifying the limit and the configuration property to adjust. |
FIRE-601 | Sonatype Repository Firewall enforcement remains active on all High Availability cluster nodes after a Zero Downtime Upgrade, with repository configuration automatically refreshed following the deferred database migration. |
FIRE-519 | The Automatic Malware Management task now completes successfully against IQ Server versions earlier than 204 by gating the quarantineEnabled field on the connected IQ Server version before sending ad-hoc evaluation requests. |
Known Issues & Upgrade Guidance
This section captures known issues in the 3.95.x line as well as upgrade guidance.
Resolved Known Issues
Impacted Version(s) | Version in which Issue is Resolved | Description |
|---|---|---|
3.95.0 – 3.95.3 & 3.96.0 | 3.95.4 & 3.96.1 | For self-hosted deployments, this issue can occur after taking both of the following actions:
Cloud deployments that use the Number of Versions field (or Retain in the API) with an affected format are also impacted. Changes to version normalization can cause components created before and after the upgrade to use different normalized version formats. When a cleanup policy uses the Number of Versions field (or Retain in the API), Nexus Repository may sort these mixed values incorrectly. As a result, the cleanup policy may select newer component versions for deletion while retaining older versions. |
3.94.0 – 3.94.1 & 3.95.0 – 3.95.2 | 3.94.2 & 3.95.3 |
Because container runtimes may use |
3.94.0 – 3.95.0 | 3.95.1 | NuGet V2 proxy repositories return locally cached results for As a workaround, delete all locally cached versions of the affected package to force the next You can also migrate the affected repository and clients to NuGet V3. |
Additional Upgrade Guidance
The 3.95.x release has a few changes that require consideration and potential action when upgrading:
Repositories where components were updated via incremental indexing (for example, tag association) while running an earlier Nexus Repository version may require a search index rebuild after upgrade to 3.95.0 in order to restore visibility for users who rely only on Repository Content Selector privileges.
Ansible Galaxy hosted repositories now return HTTP 409 Conflict (instead of 400) with a Galaxy-compatible duplicate-version error body when a duplicate collection version is published to a write-once (ALLOW_ONCE) repository; clients that explicitly expected HTTP 400 for this case should be updated.