Sonatype IQ Server 206 Release Notes
Released August 5, 2026
The IQ 206 release includes multiple changes to our IQ-powered solutions. View the details in each solution’s section below.
Ready to Upgrade?
Before upgrading, see the Known Issues & Upgrade Guidance section at the end of these release notes to determine whether any known issues or upgrade recommendations apply to your environment.
 Sonatype Lifecycle
This release includes the following changes for Sonatype Lifecycle:
Withdraw Pending Policy Waiver Requests Through the API
Policy waiver request submitters can now withdraw their own pending requests through the Policy Waiver Requests API before a reviewer approves or rejects them. This capability gives submitters greater control over requests that contain incorrect information, require additional context, or no longer apply.
Enhanced Component Identification in the HeroDevs End-of-Life Components Dashboard
Sonatype Lifecycle now provides additional component details in the HeroDevs End-of-Life Components dashboard to help teams identify and investigate affected dependencies more efficiently. The dashboard displays full component names and associated Policy Violation IDs, making it easier to distinguish similarly named components, cross-reference findings with policy violations, and move from reporting to remediation.
The dashboard also now displays complete Package URLs (PURLs) that consistently include component version information across supported package formats. These standardized, versioned identifiers make it easier to correlate end-of-life components with vulnerability databases, SBOMs, policy data, and other tools that support the PURL specification.
For full details, see the HeroDevs End of Life Components help documentation.
Support for IAM Roles for Service Accounts with Amazon S3 File Stores
Self-hosted Sonatype IQ Server deployments on Amazon Elastic Kubernetes Service (EKS) can now use IAM Roles for Service Accounts (IRSA) to authenticate with Amazon S3 file stores. IQ Server uses the AWS default credentials provider chain to retrieve temporary credentials from the IAM role associated with the Kubernetes service account, eliminating the need to store static AWS access keys in application configuration or Kubernetes secrets.
This enhancement helps organizations strengthen credential security and align IQ Server deployments with AWS-recommended identity practices. Teams can manage S3 access through IAM policies, reduce the operational overhead of rotating long-lived credentials, and use short-lived credentials that AWS automatically provides and refreshes.
 Sonatype AI Developer
AI Developer for Self-Hosted Lifecycle Customers – Preview
AI Developer is now included as a part of your Lifecycle subscription. As a valued Lifecycle customer, you are entitled to an allocation of free monthly credits for AI Developer, bringing Sonatype component intelligence, dependency guidance, and Lifecycle policy context into the AI coding assistants your developers already use through its included Model Context Protocol (MCP) server.
We wanted to get you this value as quickly as possible, so we have decided to release this as a part of version 206 in Preview mode. This means we will support you in using the AI Developer solution while we finalize some of the UI and UX work in order to deliver the polished experience we want and you deserve. Expect the capability to come out of Preview in the next one or two months.
Claim Your Credits
Contact your Sonatype account representative to claim your credits and start bringing trusted open source intelligence and policy-aware guidance into your AI-assisted development workflow.
 Sonatype Developer
This release does not include any Developer-specific changes.
 Sonatype SBOM Manager
This release does not include any SBOM Manager-specific changes.
 Sonatype Repository Firewall
This release includes the following changes for Sonatype Repository Firewall:
Firewall Success Metrics Dashboard
Sonatype Repository Firewall now includes a new Firewall Success Metrics dashboard in Enterprise Reporting, giving organizations a clearer understanding of how effectively Firewall protects their software supply chain. By bringing key operational and security insights together in one place, the dashboard helps teams measure the impact of their security policies, identify trends in component risk, and determine whether quarantine workflows are reducing exposure to malicious or vulnerable components. At a glance, teams can monitor metrics such as component evaluations, quarantines, malicious component detections, waivers, and quarantine response times to understand how Firewall is performing over time.
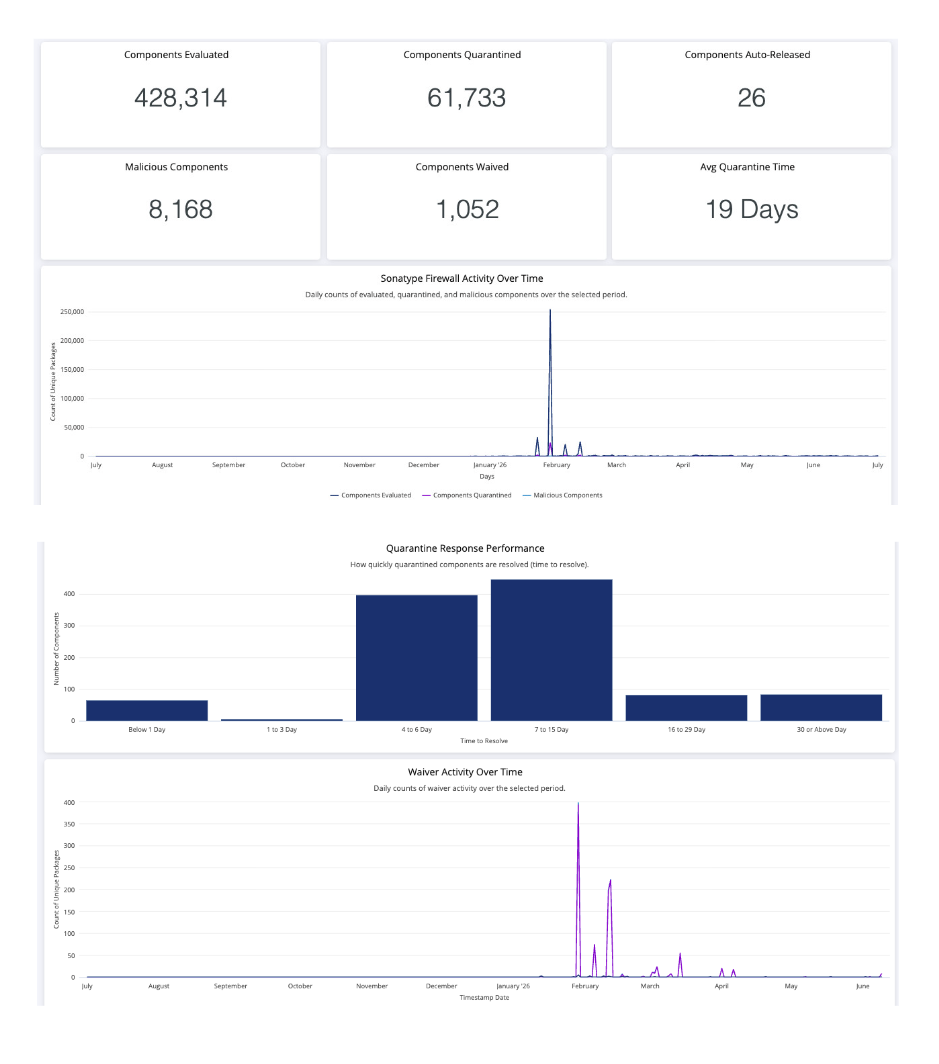 |
With greater visibility into Firewall activity, security, platform, and engineering teams can make more informed decisions about policy tuning, prioritize response efforts, and demonstrate the value of their software supply chain security program. Interactive filtering and detailed reporting make it easier to investigate quarantine trends, understand why components are blocked, monitor waiver usage, and identify opportunities to reduce review times and continuously improve how open source risk is managed across the organization.
For full details, see the Firewall Success Metrics Dashboard help documentation.
Configure the Firewall for Docker Layer Download Timeout
Sonatype Nexus Repository now lets you configure the timeout used by Firewall for Docker when downloading container image layers during policy evaluation. Previously, this timeout was fixed at 10 minutes, which could prevent image evaluation from completing in environments where legitimate network conditions, such as proxy-based antivirus scanning or other network inspection, significantly increase download times. You can now adjust the timeout to up to 240 minutes by setting the nexus.firewall.container.download.timeout.minutes system property to better accommodate your environment while maintaining Firewall for Docker protection for large or slow-to-download images.
Bug Fixes
Issue ID | Description |
|---|---|
FIRE-133 | The Firewall for Docker layer download timeout is now configurable via the |
FIRE-65 | Firewall for Docker container image scans now support a configurable layer download timeout, allowing environments with corporate AV proxies, slow WAN links, or large AI/ML images to extend beyond the previous 10-minute limit. |
CLM-42776 | Self-hosted IQ Server deployments on EKS now authenticate to S3 using IAM Roles for Service Accounts (IRSA) web identity tokens, enabling S3 file store operations without static credentials. |
CLM-42440 | Database connections are now reliably returned to the pool after any mid-stream exception, preventing connection exhaustion across all affected DAO query paths including OAuth2 and SAML login flows. |
CLM-42247 | Multiple |
CLM-40930 | Report files, scan artifacts, and policy evaluation results tied to a deleted SBOM version are now automatically removed from storage alongside the database records and SBOM blob. |
CLM-39369 | CycloneDX 1.6 XML SBOMs containing |
CLM-38159 | Vulnerability group policy conditions are now evaluated using preloaded data rather than individual database queries per component, eliminating the N+1 query pattern that caused severe slowdowns during large component metadata evaluations. |
Coming Soon
We’re excited to share that the following enhancements will be coming soon:
NeuVector-based Sonatype Container Security to be Sunset
NeuVector-based Sonatype Container Security will reach the end of its Extended Maintenance period in September 2026. To continue receiving the latest container security capabilities, plan your transition to Advanced Container Scanning (Sonatype Scanner Mode), which provides broader coverage, enhanced detection capabilities, and continued product innovation.
Known Issues & Upgrade Guidance
This section captures known issues in the IQ 206 line as well as upgrade guidance.
Resolved Known Issues
Impacted Version(s) | Version in which Issue is Resolved | Description |
|---|---|---|
IQ Server 204 – 206 | 207 | For Windows users, the |