GitHub Configuration
Creating an Access Token in GitHub
Supported GitHub Authentication
You can use either classic personal access tokens or fine-grained personal access tokens. For more information on the differences between these token types, refer to the GitHub Docs.
Basic authentication (username and password) is not supported. This method is less secure and GitHub has deprecated its use for authenticating Git operations since August 13, 2021.
Required Permissions for Tokens (classic)
Feature | Required GitHub Scope(s) |
|---|---|
| |
| |
| |
| |
|
See this explanation for details of GitHub scopes.
The items above are classic PAT scopes (coarse-grained). Fine-grained PATs use permissions instead (for example pull_requests=write).
Required Permissions for Fine-Grained Tokens
Fine-grained personal access tokens (PATs) are configured with:
Repository access: All repositories or only select repositories (a subset).
Repository permissions: What the token can do in those repos (see table below).
GitHub’s REST API surfaces the technical permission strings for fine-grained permissions via the X-Accepted-GitHub-Permissions response header (examples include pull_requests=write and contents=read). The permission-string mappings below match GitHub’s published list for fine-grained PAT permissions.
Repository Permissions
Repository Permissions | Access Levels | Permission String |
|---|---|---|
Administration | Read-only |
|
Commit statuses | Read and write |
|
Contents | Read and write |
|
Deployments | Read-only |
|
Metadata | Read-only |
|
Pull requests | Read and write |
|
How to Create the Access Token
Log in to GitHub.
In the upper-right corner, click your avatar and select Settings.
In the left menu, click Developer Settings.
In the left menu, select Fine-grained tokens or Tokens (classic).
Click the Generate new token button.
Select Generate new token for fine-grained, repo-scoped tokens, or Generate new token (classic) for general use.
Save your PAT. You will not be able to view this token again.
Protecting the Target Branch in GitHub
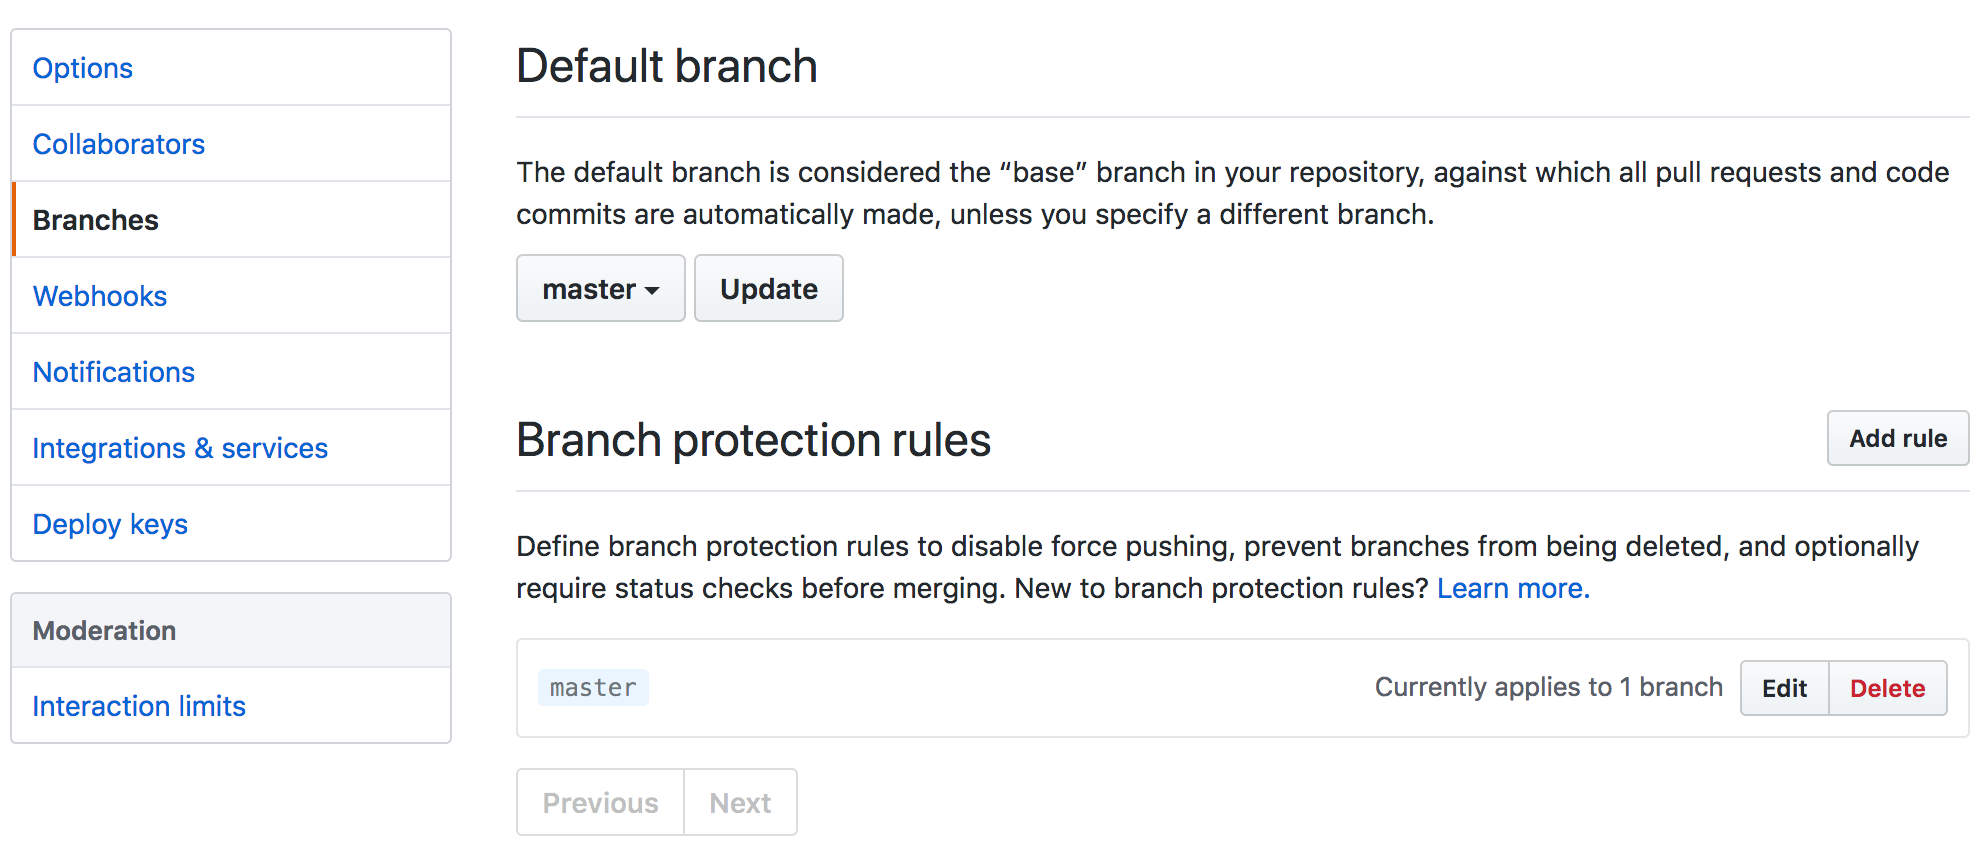
You can prevent users from merging Pull Requests with failing IQ Policy Evaluations with a Branch Protection Rule. IQ Policy Evaluations must be set to Fail at the Source Stage.
To protect a branch:
Select a Repository.
Click Settings.
Select Branches from the sidebar.
Click Add rule or edit an existing rule.
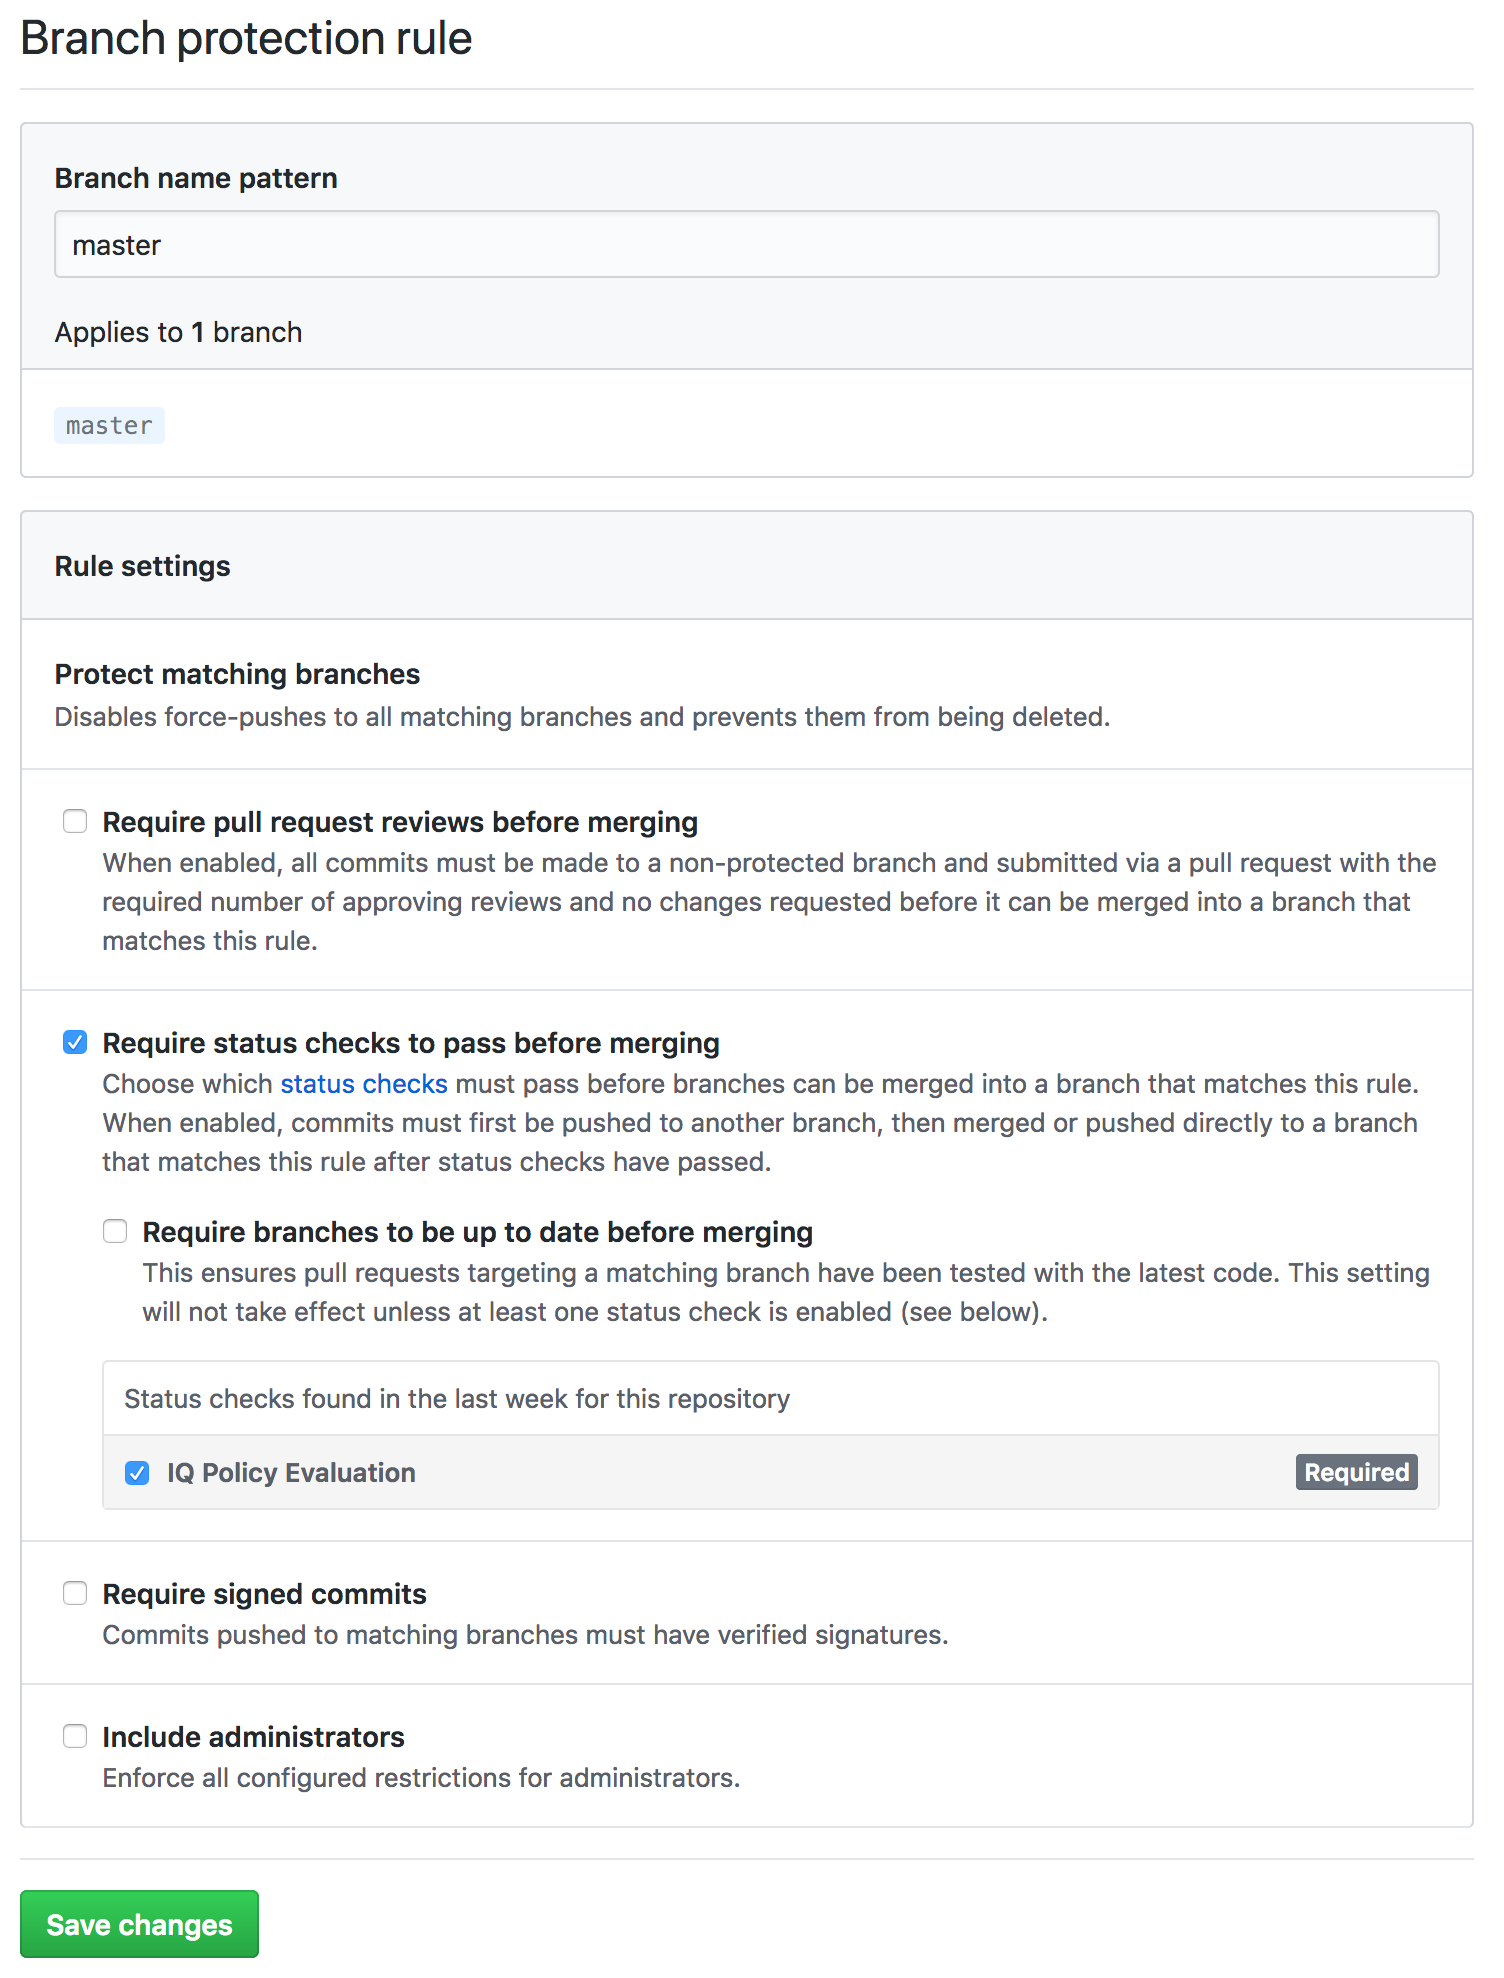
Check to Require status checks to pass before merging.
Check IQ Policy Evaluation.
Save Changes
 |
Note
The IQ Policy Evaluation status check will not appear in the list of status checks found in the last week for this repository until the first policy evaluation status has been added to the repository.
 |